Roll Out DNS Filtering in 6 Staged Steps for SMBsDNS filtering earns its place as the first thing a small or midsize business should deploy for network security. It blocks malicious and policy-violating domains at the resolver level, before an endpoint ever connects, and costs little to stand up. It won't stop threats hidden inside encrypted traffic or a compromised SaaS account, so treat it as your first layer, not your only one.
TL;DR:
- DNS filtering blocks malicious and policy-violating domains before connections are established, providing an early security layer at minimal cost.
- It relies on threat feeds and category lists checked during DNS queries, which can be bypassed if encrypted DNS protocols like DoH or DoT are not managed properly.
- Combining resolver or router deployment with endpoint agents or MDM tools offers the broadest coverage for remote and hybrid workers.
- DNS filtering cannot see inside encrypted HTTPS sessions or detect threats hosted on legitimate domains with no bad reputation, requiring supplementary security controls.
- A phased rollout with careful testing on captive portals, false positives, and OS compatibility reduces support tickets and improves deployment success.
Table of Contents
- What Is DNS Filtering for Business, and Where Does It Fit?
- How DNS Filtering Actually Works Behind the Scenes
- Which Deployment Model Fits Your Business?
- What DNS Filtering Stops, and What It Can't See
- How to Choose a DNS Filtering Solution: An SMB Checklist
- How to Roll Out DNS Filtering Without Breaking Anything
- When Managed DNS Security Makes More Sense Than DIY
- How California Telecom Supports DNS Security at Scale
- Sources
- FAQ
What Is DNS Filtering for Business, and Where Does It Fit?
DNS filtering intercepts the lookup that happens before any connection gets made. When a laptop tries to reach a domain, the resolver checks that request against threat feeds and category lists, then returns one of three outcomes: allow the connection, warn the user with a block page, or refuse it entirely by returning NXDOMAIN or redirecting to a sinkhole IP. That decision happens in milliseconds, and it happens before the device establishes a TCP connection to whatever is on the other end, according to Cloudflare's explainer on DNS filtering.
That timing is the whole point. A firewall inspects traffic that's already flowing. DNS filtering stops the flow from starting. The two controls aren't competitors, they're complementary layers that catch different things:
- DNS filtering blocks by destination, before any packet reaches the malicious host, at almost no processing cost.
- Web/content filtering inspects the actual page or file content, often after a TLS handshake, giving deeper visibility but requiring more compute and configuration.
- Firewalls control traffic by port, protocol, and IP address, catching things DNS never sees, like a direct-IP connection with no domain lookup at all.
One operational wrinkle deserves attention early: DNS-over-HTTPS (DoH) and DNS-over-TLS (DoT) encrypt the lookup itself, which can let a device bypass your configured resolver entirely if the browser or OS defaults to its own encrypted resolver. DNSSEC, meanwhile, verifies that DNS responses haven't been tampered with in transit, a separate concern from filtering but worth understanding when you're evaluating a broader DNS security posture. Most business-grade filtering products now include controls to force DoH/DoT through the managed resolver or block it outright, and you'll want to confirm that during any trial. For a deeper look at how DNS architecture supports the rest of your network, see this IT manager's guide to DNS in business networks.
How DNS Filtering Actually Works Behind the Scenes
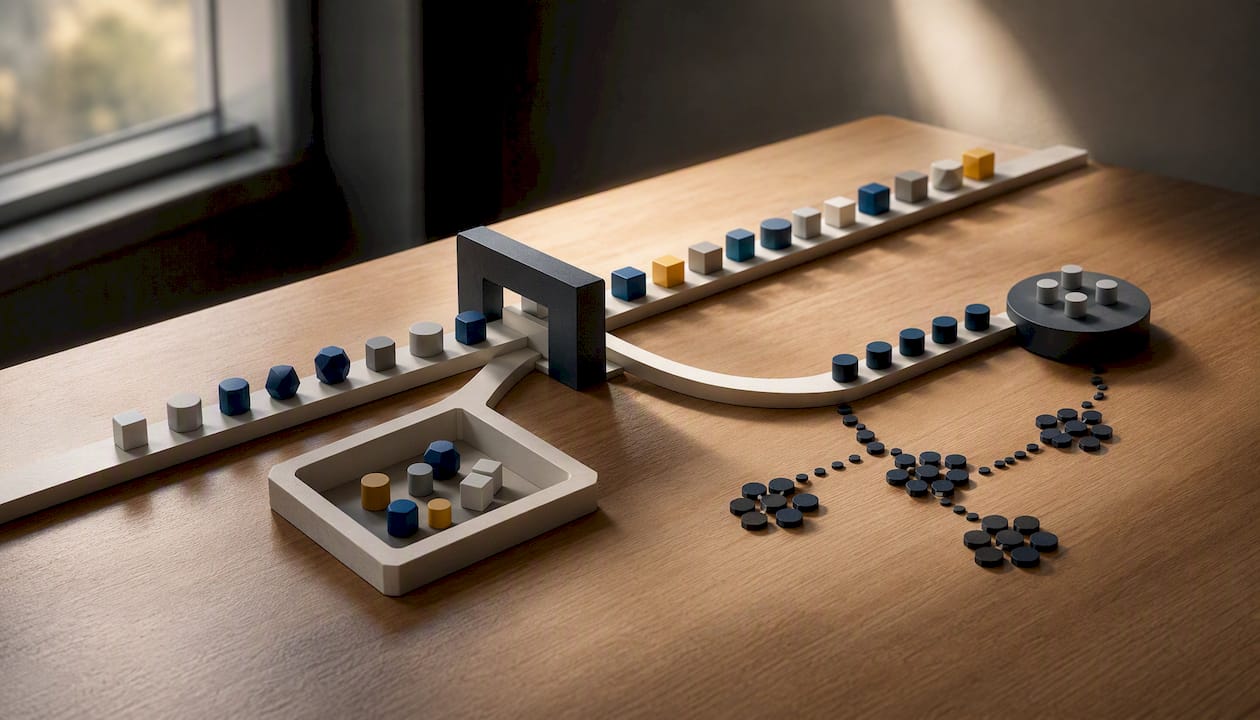
Every DNS filtering decision runs through the same basic loop, but the details matter for evaluating vendors. When a device queries a domain, the recursive resolver checks it against a set of threat intelligence feeds and category databases before returning an answer. Those feeds typically flag malware command-and-control domains, phishing infrastructure, and newly registered domains, which are disproportionately used in short-lived phishing campaigns because attackers rotate domains faster than reputation lists can catch up.
The resolver's decision happens before the client ever opens a TCP connection. That's a meaningfully different security model from an inline proxy, which has to intercept traffic that's already in motion.
What happens when a domain gets blocked comes down to a handful of response types:
- NXDOMAIN: the resolver reports the domain doesn't exist, which some applications handle gracefully and others don't.
- Sinkhole redirect: the query resolves to a controlled IP, often serving a block page, which works better for browser traffic than for background app connections.
- Silent drop: no response at all, which can cause timeouts and retries that slow down legitimate troubleshooting.
The choice between these matters more than most IT teams expect. A sinkhole that serves a friendly block page works well for a blocked shopping site during work hours. That same response type against a phishing-adjacent domain used by a background sync process can produce confusing timeout errors that generate helpdesk tickets instead of clean denials.
Logging is where DNS filtering earns its keep beyond simple blocking. Every query, allowed or denied, can be exported to a SIEM for correlation with other security events, and those logs are genuinely useful for threat hunting: DNS tunneling and domain-generation-algorithm (DGA) patterns used by malware for command-and-control often show up in query logs long before other tools notice anything wrong, per research on enterprise DNS security. If your current security stack has no DNS visibility, this alone is worth fixing before anything else.
Which Deployment Model Fits Your Business?
Businesses typically choose from four deployment models, and most end up running more than one at the same time. According to Control D's enterprise deployment guide, combining models is standard practice rather than an edge case, because no single approach covers every device in a modern, partly remote workforce.
- Resolver/DHCP-level deployment. Point your DHCP server or network resolver settings at the filtering provider's DNS. This covers every device on the local network instantly, with no software to install, but it does nothing for laptops that leave the building.
- Router/gateway deployment. Configure filtering at the edge router or firewall for the whole site. Similar coverage to the resolver model, slightly easier to manage centrally if you already have a capable gateway, but still tied to physical location.
- Endpoint agent deployment. Install a lightweight client on each device that enforces policy regardless of network. This is the only model that reliably follows remote and hybrid employees, but it adds an agent to manage, update, and troubleshoot across every operating system in your fleet.
- RMM/MDM push deployment. Use your existing remote monitoring or mobile device management platform to deploy and enforce DNS policy at scale. This is the most operationally efficient way to cover a distributed workforce if you already run an RMM or MDM tool, since you're not adding a new management console.
The practical answer for most SMBs with even one remote employee: resolver or router filtering at each physical site, plus an endpoint agent or MDM push for anyone working outside the office. That combination closes the biggest coverage gap, which is the traveling laptop that never touches your local network.
Pro Tip: Before you commit to a vendor, test three specific edge cases during your trial: how the agent behaves on a hotel or airport captive portal, whether a browser's default DoH setting silently routes around your policy, and whether the agent runs cleanly on every OS version in your actual fleet, not just the newest one.
What DNS Filtering Stops, and What It Can't See
DNS filtering earns its reputation by catching threats early and cheaply, but it has a hard ceiling on visibility that every IT decision-maker needs to understand before budgeting around it.
On the benefit side, it reliably blocks connections to known malware distribution domains, a large share of phishing infrastructure, and command-and-control channels that malware uses to phone home. It is also one of the few tools that can surface DNS tunneling, a technique attackers use to smuggle data out through DNS queries themselves, which most other security tools never inspect.
The limitations are just as real:
- It's blind to what happens inside an encrypted HTTPS session once a connection to an allowed domain is established.
- Phishing pages hosted on legitimate, unblocked domains (a compromised WordPress site, a hijacked cloud storage link) slip through because the domain itself has no bad reputation yet.
- A user or piece of malware connecting straight to an IP address, skipping DNS resolution entirely, never triggers a lookup for the filter to catch.
- Browsers or devices defaulting to encrypted DoH resolvers can bypass your configured DNS path unless you've explicitly locked that down.
Because most business traffic today is encrypted end to end, DNS filtering has to be paired with a secure web gateway or URL filtering for payload-level inspection, and with endpoint data loss prevention for account-level and file-level risks, a point made clearly in dope.security's 2026 analysis of DNS-based filtering. Think of it as the fence around the property, not the lock on every door inside.
How to Choose a DNS Filtering Solution: An SMB Checklist
Vendor marketing pages tend to blur together. What separates a filtering product that fits your business from one that creates six months of support tickets comes down to a short list of concrete, checkable criteria.
Run through these before signing anything:
- Endpoint and OS coverage: does the agent support every operating system your fleet actually runs, including older versions still in use on some machines?
- MDM/RMM integration: can you push and manage the client through the tool you already use, or does it require a separate console?
- Log export and SIEM compatibility: does it export in a format your existing security tooling can ingest, and is retention long enough for investigations?
- Policy granularity: can you set different rules by site, department, or user group, or is it one policy for everyone?
- Allowlist workflow: how fast can a legitimate site get unblocked when someone hits a false positive at 9 a.m. on a Monday?
- Captive portal handling: does the agent recognize and pass through hotel, airport, and guest Wi-Fi login pages without breaking?
- DoH/DoT controls: can the product force encrypted DNS through its own resolver, or block it, so users can't accidentally bypass policy?
- SLA and support model: what's the guaranteed response time, and is support staffed by people who understand DNS, not just a ticket queue?
For validation, don't take a sales deck's word for any of this. Run the product in log-only mode against real traffic for two to four weeks, count how many false positives show up against your actual business-critical domains, and stress-test the agent through an update cycle to see if it survives OS patches without breaking.
Pro Tip: Ask every vendor for their false-positive rate on newly registered domains specifically. That category catches the most legitimate new vendor sites and partner portals, and it's where most helpdesk friction during rollout actually comes from.
Budget-wise, SMB DNS filtering pricing generally follows a per-seat or per-device monthly model, sometimes tiered by feature set (basic category blocking versus full threat intelligence and SIEM export). Total cost of ownership includes more than the license: factor in the staff time for policy tuning, allowlist management, and the agent rollout itself, especially in the first quarter.
How to Roll Out DNS Filtering Without Breaking Anything
Most DNS filtering failures aren't technology failures, they're rollout failures. Turning on aggressive blocking for the entire company on day one is the single most common way to generate a flood of angry tickets and get the whole project shelved. A phased approach avoids that.
- Inventory first. Map your internal DNS zones, list domains that are business-critical (payment processors, SaaS tools, partner portals), and confirm which management tool (MDM, RMM, group policy) you'll use to push the client.
- Pilot in log-only mode. Turn on logging without any blocking for a small group, ideally two to four weeks, so you can see real query patterns before anything gets denied, a step Control D's deployment guide treats as non-negotiable for avoiding rollout breakage.
- Enable high-confidence blocks first. Turn on blocking for malware and phishing categories, the ones with the lowest false-positive risk, before touching anything more subjective like content categories.
- Add categories incrementally. Layer in additional policy categories (gambling, adult content, social media, whatever fits your acceptable use policy) one at a time, watching for helpdesk volume after each change.
- Roll out site by site, or team by team. Push the agent through MDM/RMM to remote and mobile users in waves rather than all at once, so any breakage is contained to a small group you can fix quickly.
- Build ongoing operations. Set a quarterly cadence to review the allowlist, retune alert thresholds, and check that new SaaS tools your business has adopted aren't getting caught in category blocks.
During the pilot phase specifically, capture your top NXDOMAIN results and highest-frequency domains, and cross-reference them against your list of business-critical services before you flip any switch to "block." That single step catches most of the false positives that would otherwise surface in week one of enforcement.
When Managed DNS Security Makes More Sense Than DIY
Self-managing DNS filtering works fine for a single office with a small, static device count. It gets harder fast once you're running multiple sites, a remote workforce, and a helpdesk that's already stretched thin on tickets.
That's the gap managed network services close. Running Managed SD-WAN across sites means DNS policy travels with a centrally managed network fabric instead of living on a config sheet for each location, and a 24/7 U.S.-based NOC means someone's watching the logs at 2 a.m., not just during business hours. For a business running three retail locations plus a dozen remote sales reps, that combination turns a months-long rollout project into something closer to a checklist.
— Jim
How California Telecom Supports DNS Security at Scale
Rolling out DNS filtering across multiple locations and a remote workforce is a networking project as much as a security one, and that's exactly where a single-vendor approach pays off. A single-vendor approach helps avoid juggling separate DNS, firewall, and connectivity vendors by designing and deploying DNS policy across sites, backed with 24/7 U.S.-based NOC support, and providing consolidated billing and support contacts instead of multiple queues.Our Managed LAN/WAN and Managed SD-WAN services carry resolver policy to every branch site under a 99.99% uptime SLA on data, while our managed services bundle, including firewall services and continuous Netverge monitoring, gives you the layered defense DNS filtering alone can't provide. Rollout support generally includes integration with MDM/RMM tools and allowlist management handled by experienced engineers rather than generic ticket queues.
If you're planning a multi-site DNS security rollout and want it handled by people who deploy this for a living, book a consultation and we'll walk through what a phased implementation looks like for your specific footprint.
Sources
- What is DNS filtering? | Secure DNS servers
- DNS Filtering for Enterprise IT: Deployment Guide | Control D
- Dope
FAQ
Which DNS Filtering Services Are the Best for a Business?
The best option depends on your fleet size and how many remote users you have, since coverage model matters more than any single feature list. Prioritize vendors that support MDM/RMM push, SIEM log export, and a fast allowlist process, and validate all three in a log-only pilot before committing, as recommended in Control D's enterprise deployment guide.
How Much Does DNS Filtering Cost for a Business?
Most SMB DNS filtering products price per seat or per device on a monthly basis, often with tiers separating basic category blocking from full threat intelligence and SIEM export. Californiatelecom doesn't publish flat DNS filtering pricing since it's typically bundled into a broader managed services or Managed SD-WAN engagement, so pricing is available on request based on site count and coverage needs.
What Is the Best Web Filtering Software for a Small Business?
There's no single best answer, because web filtering (which inspects page content) and DNS filtering (which blocks by destination before a connection starts) solve different problems and work best together. For most small businesses, the practical answer is DNS filtering for broad, low-overhead coverage, paired with a secure web gateway for the encrypted traffic DNS filtering can't inspect, per Dope.
What Is a Business DNS, and Why Does It Matter for Security?
A business DNS setup is the resolver infrastructure a company uses to translate domain names into IP addresses for every device on its network, and it's a natural checkpoint for security policy because every connection has to pass through it first. Filtering at that checkpoint blocks malicious and policy-violating domains before a device connects, according to Cloudflare, making it one of the cheapest, fastest security controls an SMB can deploy.